INDEPENDENT RESEARCH LAB
0x7ouda
Initializing workspace...
DIGITAL FORENSICS / RESEARCH ARCHIVE

Observing.Investigating.Documenting.

+THE PURSUIT OF UNDERSTANDING+
The investigator and the elusive evidenceA persistent investigator with a magnifying glass follows a mischievous green virus between evidence markers. The scene can be paused using the button below.0102TRACE FOUNDOBSERVE.CORRELATE.UNDERSTAND.
# EXPLORE BY TAG
#The art of memory forensics4#HackTheBox3#ECDFP_Notes2#Blockchain1#CAT Reloaded CTF 261#CTF1#Drone_Forensics1#encrypted_disk1#Malware Analysis1#Memory_Forensics1#OSINT1#Splunk1
01 / FROM THE LAB

Latest findings.

All research

All dispatches

OBSERVATIONS → UNDERSTANDING
The Art of Memory Forensics
Note

The Art of Memory Forensics Chapter-05

Brief notes summarizing Chapter 5 of (AMF), focusing on Windows objects, kernel pool allocations, pool tags, pool-scanning techniques, Big Page Pool analysis, and alternative methods for locating kernel objects.
The art of memory forensics
9 min read
The Art of Memory Forensics
Note

The Art of Memory Forensics Chapter-04

Brief notes summarizing Chapter 4 of The Art of Memory Forensics, focusing on memory acquisition methods, dump formats, virtual machine memory, memory conversion, and volatile evidence stored on disk.

The art of memory forensics
8 min read
The Art of Memory Forensics
Note

The Art of Memory Forensics Chapter-02

Brief notes summarizing Chapter 2 of The Art of Memory Forensics, focusing on different data structures, how they are organized and stored in memory, and how they are interpreted during memory analysis.

The art of memory forensics
8 min read
The Art of Memory Forensics
Note

The Art of Memory Forensics Chapter-01

Brief notes summarizing Chapter 1 of The Art of Memory Forensics, with a focus on system overview and core operating system concepts.

The art of memory forensics
16 min read
CTF
Case writeup

Glyph — DFIR Investigation Lab | CAT Reloaded CTF 2026

A DFIR walkthrough of the Glyph challenge, tracing a Unicode homograph phishing chain through browser artifacts, PowerShell, NTFS, SRUM, malware execution, C2 activity, and persistence.

CTFCAT Reloaded CTF 26
10 min read
Blockchain Security
Research

From DNS Hijacking to Stealing Over $600K

A blockchain security investigation into the 2022 Curve Finance DNS hijacking attack, tracing the malicious approval flow and calculating the stolen funds.

Blockchain
4 min read
ECDFP_Notes
Note

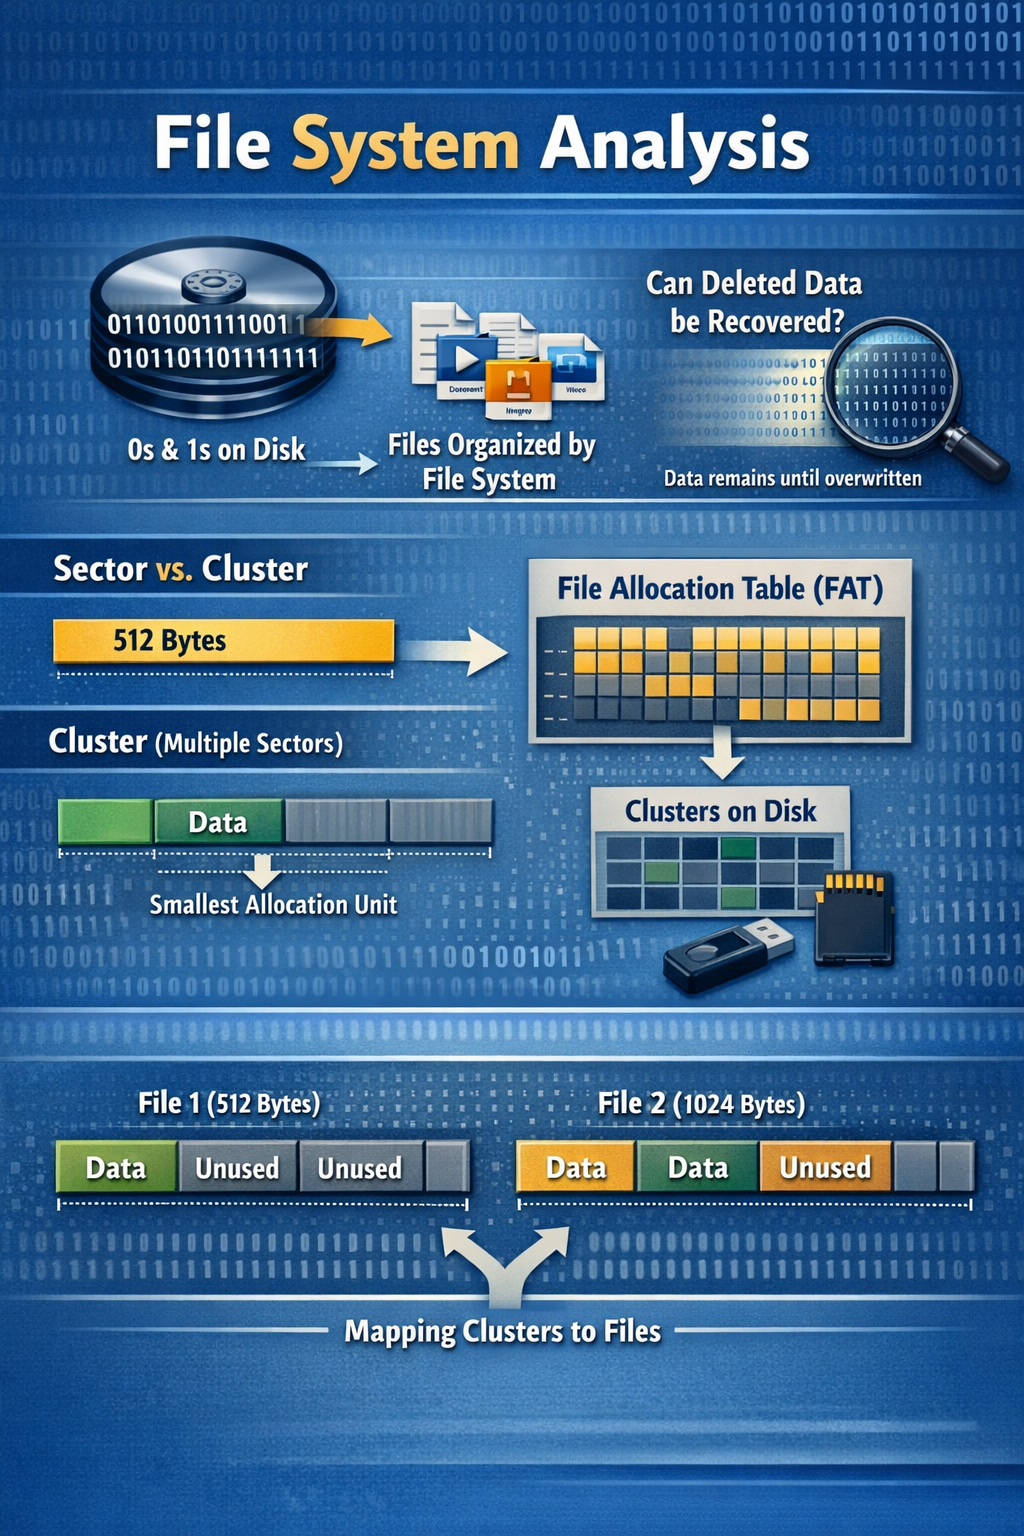
File Systems Analysis From ECDFP

A concise guide to file system forensics, covering FAT and NTFS structures, deleted file recovery, file carving, and practical tools like SleuthKit, Autopsy, and PhotoRec.

ECDFP_Notes
11 min read
Malware Analysis
Tool

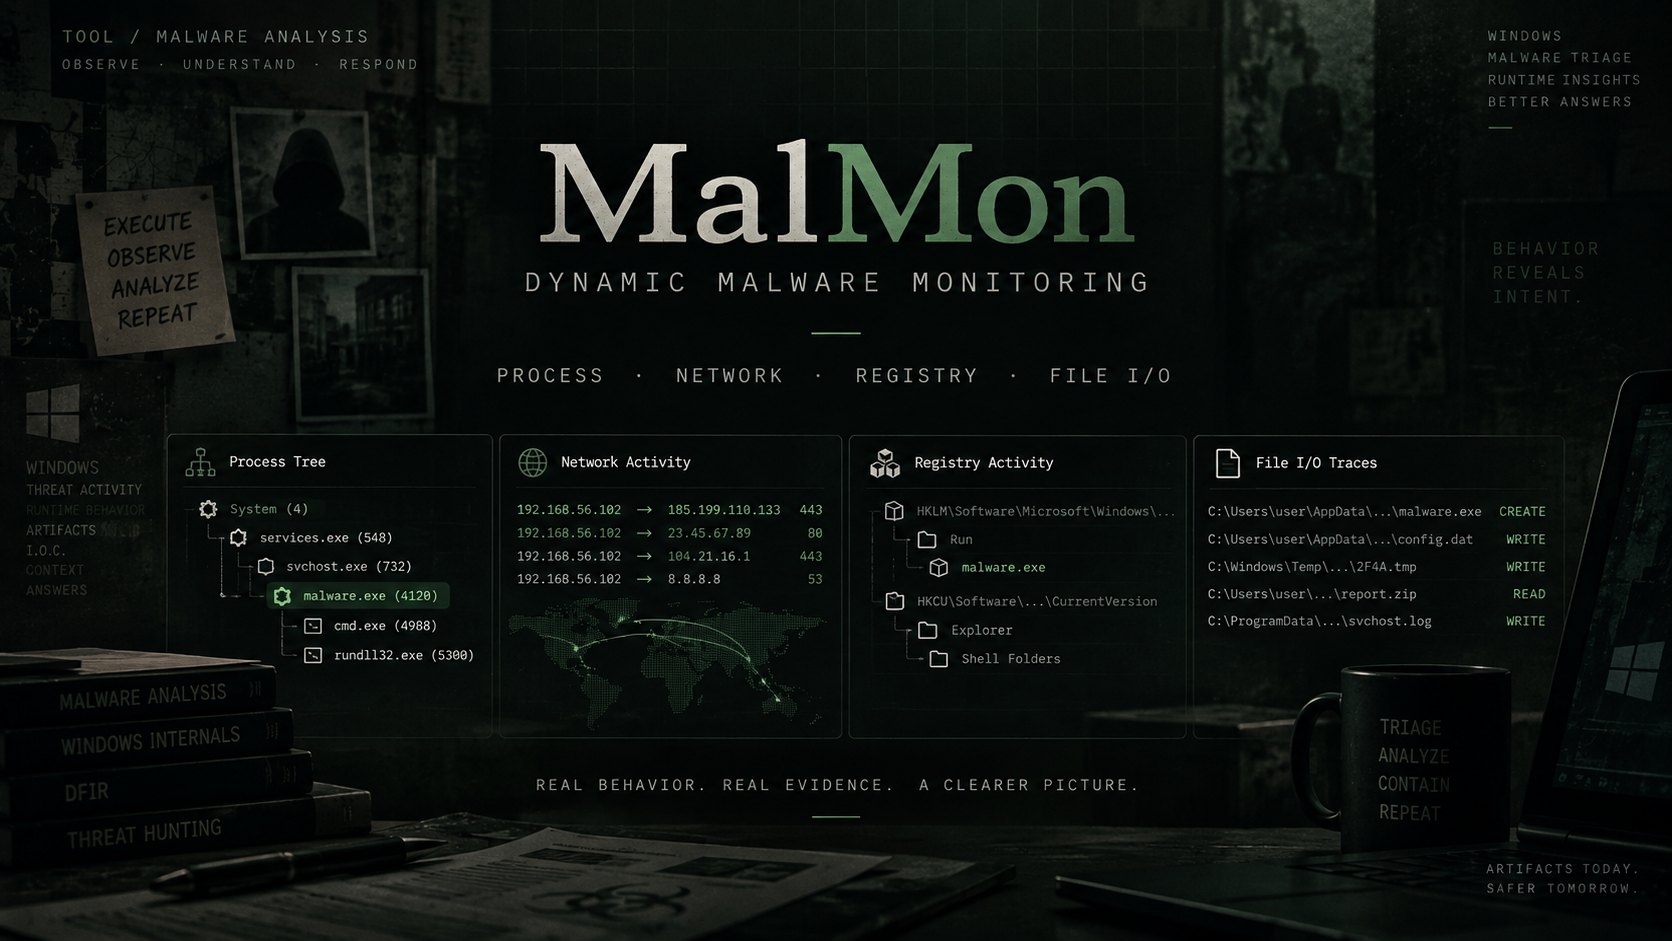
MalMon

A Windows-focused dynamic malware analysis and triage tool that monitors process trees, command lines, network connections, registry activity, and file I/O, then exports structured HTML and JSON reports.

Malware Analysis
3 min read
ECDFP_Notes
Note

Disk forensics notes from ECDFP

ECDFP notes covering disk forensics fundamentals, CHS/LBA addressing, MBR and GPT structures, boot records, and partition analysis with practical hex examples.

ECDFP_Notes
8 min read
HackTheBox
Case writeup

AoTR 4: A Drone in the Snow

A recovered disk blew the case open. The files inside weren't theory, they were a checklist. Hours later, an unmarked matte-black drone was found half-buried in snow in Budapest,

HackTheBoxDrone_Forensics
5 min read
HackTheBox
Case writeup

AoTR 3 The Abandoned Farmhouse

The coordinates led police and investigator into winter, to a place far enough from everything that no one would notice if something went wrong.

HackTheBoxencrypted_disk
11 min read
Splunk
Note

Splunk Detection Rule AND Generate Alert

A practical SOC home lab guide to building Splunk detection rules and alerts for XSS, command injection, and SQL injection attacks.

Splunk
6 min read
HackTheBox
Case writeup

HackTheBox The Tunnel Without Walls

A memory dump from a connected Linux machine reveals covert network connections, fake services, and unusual redirects. Holmes investigates further to uncover how the attacker is manipulating the entire network!

HackTheBoxMemory_Forensics
5 min read